---
title: Ransomware Simulator Script – A tool for testing ransomware defenses
description: Simulate a ransomware attack. Use two PowerShell scripts to simulate a ransomware attack. One script to encrypt the data and another to decrypt the data.
image: https://blog.canauri.com/hubfs/CryptoStopper/encrypting%20files.png
---
- [319-383-0165](tel:+1.319-383-0165)
- [Free Tools](https://www.getcryptostopper.com/free-tools)
- [About](https://www.getcryptostopper.com/about)
- [Partners](https://www.getcryptostopper.com/partners)
[](https://www.getcryptostopper.com/)
- [CryptoStopper™](https://www.getcryptostopper.com/cryptostopper/)
- [For MSPs](https://www.getcryptostopper.com/cryptostopper-for-msps/)
- [Blog](https://blog.getcryptostopper.com/)
[Pricing](https://www.getcryptostopper.com/pricing)
# Ransomware Simulator Script – A tool for testing ransomware defenses
November 18, 2019 [Nathan Studebaker](https://blog.canauri.com/author/nathan-studebaker)
For too long, consumers have been without a method to test the cyber security products that they are purchasing or evaluating. Instead, the products are ‘field tested’ during a real event, at which time it’s revealed that the products didn’t perform as expected. WatchPoint is disrupting the cyber security market by providing all consumers with a way to test their defenses before it’s too late.
## Ransomware simulations
There is really no shortcut for something like this. It's not enough to just know what files could be encrypted, and you certainly don't need a tool to tell you that. What you need is a ransomware simulator that can safely encrypt some files on your computer, to let you know if your defenses are actually working.
At WatchPoint, we’ve developed a PowerShell script that will encrypt data on your server, workstation or laptop, but in a way that's under your control, has an off switch and allows you to decrypt the data as well. It has the potential to do as much harm as the delete button on your keyboard, but when used correctly it can be an invaluable tool that will uncover the answer to the important question of whether or not your security products are working.
## Overview
We have written two PowerShell scripts that function just like ransomware. One script encrypts the data, and the other script decrypts the data using a public/private key pair. We created these as a tool so that you can test your defenses against the real thing. The purpose of the decrypter is to ensure that your files aren't permanently destroyed.
Here is an overview of how it works.
###USE AT YOUR OWN RISK - THESE SCRIPTS ARE PROVIDED FREE OF CHARGE - WATCHPOINT DOES NOT PROVIDE SUPPORT FOR THESE SCRIPTS. THIS IS A FREE TOOL FOR TESTING PURPOSES ONLY. DO NOT RUN IN A PRODUCTION ENVIRONMENT.###
[](https://hubspot-cta-redirect-na2-prod.s3.amazonaws.com/cta/redirect/604281/8d29d3ec-c2f6-4ab8-99df-a2fe864fd9a5)
- First, you must have a certificate. I’ve included one in the download for ease of use.
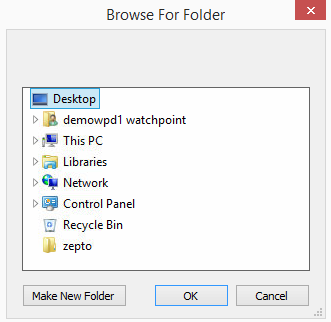
- When you run the script, a dialog box will open, prompting you to choose the folder you’d like to attack. This could be a single folder on the desktop, the entire desktop, or any folder you’d like.
- All files are discovered.
- Each file is encrypted with the Public key of the certificate.
- After all the files have been encrypted, the script exits.
The decryption script does the same thing, except that it decrypts files instead of encrypting them. The script also makes a copy of every file before it encrypts them. It stores the copy in env:temp. It should go without saying, but please make sure you have a good backup before running this ransomware simulator, as the files will be encrypted.
Make sure that you have permission. WatchPoint is not responsible for any outcome of running these scripts. If you know what you're doing, then it's safe, if not then please don't do it! Also, here is a [link](https://www.getcryptostopper.com/ransomware-simulator/) to some other similar tools we’ve created.
Here are the steps to run the ransomware simulation:
## The Environment:
This script, just like actual ransomware, will encrypt files very quickly. Because of this, you need to configure your test folder with a minimum number of folders and files. We recommend three subfolders, with 100 files each, for a total of 300 files.
- To run the simulation, you'll need a Windows workstation or laptop. Windows 7 SP1, Windows 8, 8.1 and Windows 10 are supported.
- You need a folder containing data and subfolders for testing. We recommend a minimum of three subfolders with 100 files each. To make things easier, you can use the random file generator script included in the download.
## The Simulation
As mentioned previously, you’re going to need a test computer from which to run the simulation. In my example, I am using a Windows 8 computer, but Windows 7 and Windows 10 will work just fine.
1. Make sure that you have a good backup.
2. Double check that you do indeed have a good backup.
3. Extract all files in the ransomware\_simulation\_scripts.zip. The password to open the zip file is ***watchpoint***
4. Before we can run the script, we have to provide it a certificate to use.
5. In this step, I’ll show you how to import the certificate, but if you already have one that you’d like to use, then you can skip this step.
- Double-click the certificate that is included in the download. You’ll be presented with the ‘Certificate Import '
- Click Next \> Next again. 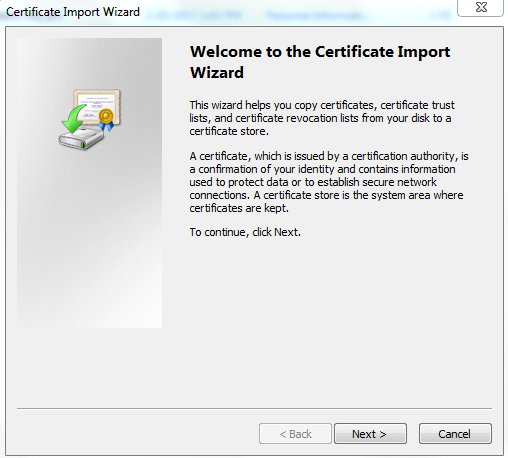
- Enter the password for the private key. The password is intentionally simple, for ease of use purposes. The password is: ***mypassword123***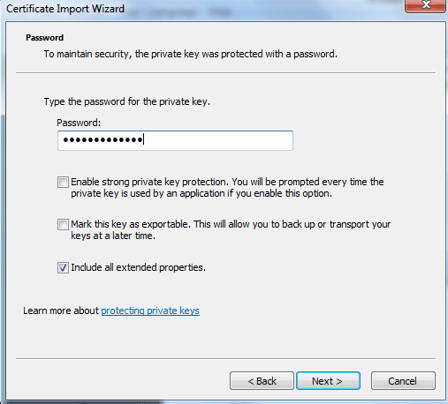
- Click Next \> Next again \> Finish.
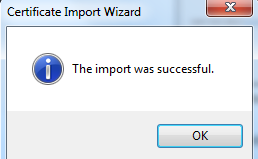
- You’ll be presented with a confirmation.
- 
Get-childitem cert:\\currentuser\\my
6. Now we need to identify the thumbprint of our certificate.
7. Open an administrative PowerShell prompt and enter the following command: Get-childitem cert:\\currentuser\\my 
8. You should see output similar to what is below. 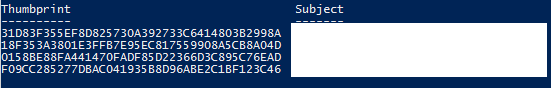
9. Copy the thumbprint id to the PowerShell scripts, see below:
**Before:**
****
**After:**
****
9\. Next, set up the test folder to use for the simulation.
10\. Additionally, let’s create a test file in our test folder and enter some text. The text will be encrypted after we run our simulation.
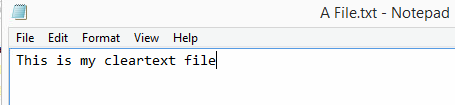11. Now it’s time to run the PowerShell ransomware/encryption script. Right click the script and select ‘Run with PowerShell.'
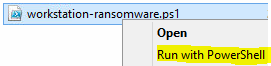
12\. You are presented with a ‘Browse For Folder’ window. From here select the test folder that you want to encrypt and then select OK.
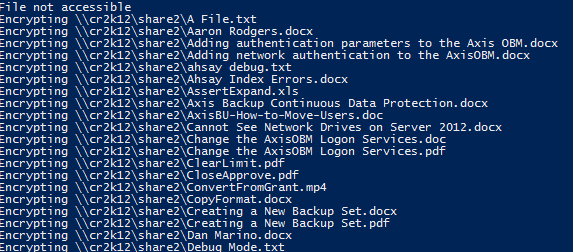
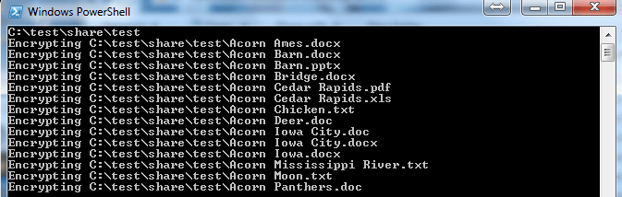
13\. You should immediately start seeing output like this:
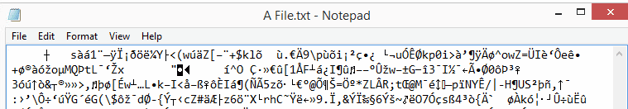
14. Now let’s check our plain text file. As you’ll see it’s not clear-text anymore, which means the encryption worked!
But the big question is, did your defenses work? Was the ransomware attack blocked or were all the files encrypted? Only you can answer that question, but if you had [CryptoStopper](https://www.getcryptostopper.com/cryptostopper-tour), then it definitely did!
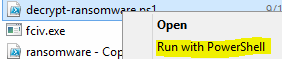
15\. Next, use the decrypt script to decrypt your files. Just like before, right-click the script and select ‘Run with PowerShell.'
16. Presto! The original file is back!
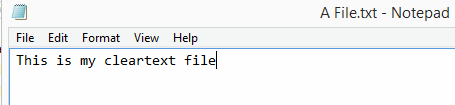
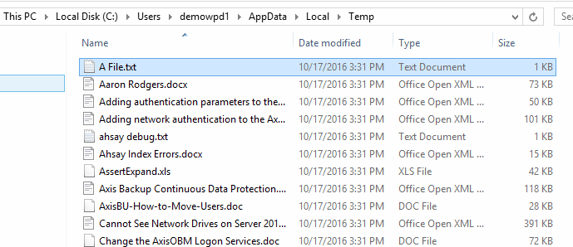
17. On a side note, and as I mentioned earlier, the script makes a copy of every file it encrypts to the env:temp directory, aka C:\\users\\username\\AppData\\Local\\Temp. So if you didn’t heed the warnings in steps 1 and 2, check this directory for a copy of the files, just in case the decryption didn’t work.
That’s it. You now have a simple and effective way to test the security of your computer against an attack. And because we have the decrypter, you can undo the effects of the simulated attack. Put [CryptoStopper](https://www.getcryptostopper.com/cryptostopper-tour) to the test - download a free trial and protect your valuable data.
###USE AT YOUR OWN RISK - THESE SCRIPTS ARE PROVIDED FREE OF CHARGE - WATCHPOINT DOES NOT PROVIDE SUPPORT FOR THESE SCRIPTS. THIS IS A FREE TOOL FOR TESTING PURPOSES ONLY. DO NOT RUN IN A PRODUCTION ENVIRONMENT.###
[](https://hubspot-cta-redirect-na2-prod.s3.amazonaws.com/cta/redirect/604281/8d29d3ec-c2f6-4ab8-99df-a2fe864fd9a5)
### Share this:
- [Tweet](https://twitter.com/share)
[Previous Post Raccoon Stealer Malware Service Gaining Popularity](https://blog.canauri.com/raccoon-stealer-malware-service-gaining-popularity) [Next Post Managed Service Providers Hit With Ransomware Attacks](https://blog.canauri.com/managed-service-providers-hit-with-ransomware-attacks)
[](https://www.entrepreneur.com/article/286698)
### Share
[](http://www.facebook.com/share.php?u=https%3A%2F%2Fblog.canauri.com%2Fransomware-simulator-script%3Futm_medium%3Dsocial%26utm_source%3Dfacebook) [](http://www.linkedin.com/shareArticle?mini=true&url=https%3A%2F%2Fblog.canauri.com%2Fransomware-simulator-script%3Futm_medium%3Dsocial%26utm_source%3Dlinkedin) [](https://twitter.com/intent/tweet?original_referer=https%3A%2F%2Fblog.canauri.com%2Fransomware-simulator-script%3Futm_medium%3Dsocial%26utm_source%3Dtwitter&url=https%3A%2F%2Fblog.canauri.com%2Fransomware-simulator-script%3Futm_medium%3Dsocial%26utm_source%3Dtwitter&source=tweetbutton&text=Ransomware%20Simulator%20Script%20%E2%80%93%20A%20tool%20for%20testing%20ransomware%20defenses) [](http://pinterest.com/pin/create/button/?url=https%3A%2F%2Fblog.canauri.com%2Fransomware-simulator-script%3Futm_medium%3Dsocial%26utm_source%3Dpinterest&media=) [](mailto:?subject=Check%20out%20https%3A%2F%2Fblog.canauri.com%2Fransomware-simulator-script%3Futm_medium%3Dsocial%26utm_source%3Demail%20&body=Check%20out%20https%3A%2F%2Fblog.canauri.com%2Fransomware-simulator-script%3Futm_medium%3Dsocial%26utm_source%3Demail)
### Subscribe to Email Updates
### Recent Posts
### Posts by Topic
- [Cyber Threats (164)](https://blog.canauri.com/topic/cyber-threats)
- [Ransomware (91)](https://blog.canauri.com/topic/ransomware)
- [Data Breach (68)](https://blog.canauri.com/topic/data-breach)
- [Business (49)](https://blog.canauri.com/topic/business)
- [Scams (19)](https://blog.canauri.com/topic/scams)
- [cybersecurity (14)](https://blog.canauri.com/topic/cybersecurity)
- [Cyber Attack (10)](https://blog.canauri.com/topic/cyber-attack)
- [Uncategorized (9)](https://blog.canauri.com/topic/uncategorized)
- [Breach (8)](https://blog.canauri.com/topic/breach)
- [Data (8)](https://blog.canauri.com/topic/data)
- [Phishing (7)](https://blog.canauri.com/topic/phishing)
- [cyber (5)](https://blog.canauri.com/topic/cyber)
- [decrypters (5)](https://blog.canauri.com/topic/decrypters)
- [security (5)](https://blog.canauri.com/topic/security)
- [Insider (4)](https://blog.canauri.com/topic/insider)
- [Ransomware Decrypters (4)](https://blog.canauri.com/topic/ransomware-decrypters)
- [cybercrime (4)](https://blog.canauri.com/topic/cybercrime)
- [managed service providers (4)](https://blog.canauri.com/topic/managed-service-providers)
- [ransom (4)](https://blog.canauri.com/topic/ransom)
- [ransomware ransom (4)](https://blog.canauri.com/topic/ransomware-ransom)
- [Banking Trojans (3)](https://blog.canauri.com/topic/banking-trojans)
- [Firewalls (3)](https://blog.canauri.com/topic/firewalls)
- [Press Release (3)](https://blog.canauri.com/topic/press-release)
- [Ransomware as a Service (3)](https://blog.canauri.com/topic/ransomware-as-a-service)
- [WannaCry (3)](https://blog.canauri.com/topic/wannacry)
- [Zero Day Vulnerability (3)](https://blog.canauri.com/topic/zero-day-vulnerability)
- [business email compromise (3)](https://blog.canauri.com/topic/business-email-compromise)
- [cyber security (3)](https://blog.canauri.com/topic/cyber-security)
- [decryptors (3)](https://blog.canauri.com/topic/decryptors)
- [ransomware attack (3)](https://blog.canauri.com/topic/ransomware-attack)
- [BlueKeep (2)](https://blog.canauri.com/topic/bluekeep)
- [CEO fraud (2)](https://blog.canauri.com/topic/ceo-fraud)
- [COVID-19 (2)](https://blog.canauri.com/topic/covid-19)
- [COVID-19 cybersecurity (2)](https://blog.canauri.com/topic/covid-19-cybersecurity)
- [Cyberattack (2)](https://blog.canauri.com/topic/cyberattack)
- [Fileless (2)](https://blog.canauri.com/topic/fileless)
- [Fileless Malware (2)](https://blog.canauri.com/topic/fileless-malware)
- [Fileless Ransomare (2)](https://blog.canauri.com/topic/fileless-ransomare)
- [Fortnite vulnerability (2)](https://blog.canauri.com/topic/fortnite-vulnerability)
- [MSPs (2)](https://blog.canauri.com/topic/msps)
- [Patch (2)](https://blog.canauri.com/topic/patch)
- [Small and Medium Enterprises Cybersecurity (2)](https://blog.canauri.com/topic/small-and-medium-enterprises-cybersecurity)
- [Spear Phishing (2)](https://blog.canauri.com/topic/spear-phishing)
- [WFH (2)](https://blog.canauri.com/topic/wfh)
- [Wi-Fi Connections (2)](https://blog.canauri.com/topic/wi-fi-connections)
- [Zero Day (2)](https://blog.canauri.com/topic/zero-day)
- [Zero Day Attacks (2)](https://blog.canauri.com/topic/zero-day-attacks)
- [bitcoin (2)](https://blog.canauri.com/topic/bitcoin)
- [bitcoins (2)](https://blog.canauri.com/topic/bitcoins)
- [cryptocurrency (2)](https://blog.canauri.com/topic/cryptocurrency)
- [cryptocurrency mining (2)](https://blog.canauri.com/topic/cryptocurrency-mining)
- [cryptojacking (2)](https://blog.canauri.com/topic/cryptojacking)
- [cyber attacks on hospitals (2)](https://blog.canauri.com/topic/cyber-attacks-on-hospitals)
- [cybersecurity jobs (2)](https://blog.canauri.com/topic/cybersecurity-jobs)
- [defray (2)](https://blog.canauri.com/topic/defray)
- [defray ransomware (2)](https://blog.canauri.com/topic/defray-ransomware)
- [fortnite (2)](https://blog.canauri.com/topic/fortnite)
- [gandcrab ransomware (2)](https://blog.canauri.com/topic/gandcrab-ransomware)
- [hacking (2)](https://blog.canauri.com/topic/hacking)
- [health (2)](https://blog.canauri.com/topic/health)
- [healthcare (2)](https://blog.canauri.com/topic/healthcare)
- [hospital cybersecurity (2)](https://blog.canauri.com/topic/hospital-cybersecurity)
- [mac malware (2)](https://blog.canauri.com/topic/mac-malware)
- [municipalities cyberattack (2)](https://blog.canauri.com/topic/municipalities-cyberattack)
- [municipalities ransomware (2)](https://blog.canauri.com/topic/municipalities-ransomware)
- [passwords (2)](https://blog.canauri.com/topic/passwords)
- [ransomware attacks (2)](https://blog.canauri.com/topic/ransomware-attacks)
- [ransomware normal (2)](https://blog.canauri.com/topic/ransomware-normal)
- [scareware (2)](https://blog.canauri.com/topic/scareware)
- [two-factor authentication (2)](https://blog.canauri.com/topic/two-factor-authentication)
- [2018 cybersecurity (1)](https://blog.canauri.com/topic/2018-cybersecurity)
- [2018 cybersecurity review (1)](https://blog.canauri.com/topic/2018-cybersecurity-review)
- [2019 cybersecurity predictions (1)](https://blog.canauri.com/topic/2019-cybersecurity-predictions)
- [2019 predictions (1)](https://blog.canauri.com/topic/2019-predictions)
- [2020 Cybersecurity Predictions (1)](https://blog.canauri.com/topic/2020-cybersecurity-predictions)
- [2FA (1)](https://blog.canauri.com/topic/2fa)
- [Arizona (1)](https://blog.canauri.com/topic/arizona)
- [Arizona beverages ransomware (1)](https://blog.canauri.com/topic/arizona-beverages-ransomware)
- [BEC (1)](https://blog.canauri.com/topic/bec)
- [BEC Attacks (1)](https://blog.canauri.com/topic/bec-attacks)
- [BitPaymer (1)](https://blog.canauri.com/topic/bitpaymer)
- [BlueKeep Exploit (1)](https://blog.canauri.com/topic/bluekeep-exploit)
- [BlueKeep Vulnerability (1)](https://blog.canauri.com/topic/bluekeep-vulnerability)
- [CISO (1)](https://blog.canauri.com/topic/ciso)
- [Chief Information Security Officer (1)](https://blog.canauri.com/topic/chief-information-security-officer)
- [Coronavirus (1)](https://blog.canauri.com/topic/coronavirus)
- [Coronavirus scams (1)](https://blog.canauri.com/topic/coronavirus-scams)
- [CryptoMix (1)](https://blog.canauri.com/topic/cryptomix)
- [Cyber Liability Insurance (1)](https://blog.canauri.com/topic/cyber-liability-insurance)
- [DLL (1)](https://blog.canauri.com/topic/dll)
- [DLL CryptoMix (1)](https://blog.canauri.com/topic/dll-cryptomix)
- [Data Leak (1)](https://blog.canauri.com/topic/data-leak)
- [Deepfakes (1)](https://blog.canauri.com/topic/deepfakes)
- [Dridex (1)](https://blog.canauri.com/topic/dridex)
- [ERP (1)](https://blog.canauri.com/topic/erp)
- [ERP Systems (1)](https://blog.canauri.com/topic/erp-systems)
- [Enterprise Resource Planning (1)](https://blog.canauri.com/topic/enterprise-resource-planning)
- [Exactis (1)](https://blog.canauri.com/topic/exactis)
- [FIFA (1)](https://blog.canauri.com/topic/fifa)
- [Fortnite ransomware (1)](https://blog.canauri.com/topic/fortnite-ransomware)
- [GandCrab (1)](https://blog.canauri.com/topic/gandcrab)
- [Google (1)](https://blog.canauri.com/topic/google)
- [Have I been pwned (1)](https://blog.canauri.com/topic/have-i-been-pwned)
- [Hospitals Ransomware (1)](https://blog.canauri.com/topic/hospitals-ransomware)
- [Kirk (1)](https://blog.canauri.com/topic/kirk)
- [Kirk Ransomware (1)](https://blog.canauri.com/topic/kirk-ransomware)
- [LockBit (1)](https://blog.canauri.com/topic/lockbit)
- [LockerGoga (1)](https://blog.canauri.com/topic/lockergoga)
- [LockerGoga Ransomware (1)](https://blog.canauri.com/topic/lockergoga-ransomware)
- [M&A (1)](https://blog.canauri.com/topic/ma)
- [Malware (1)](https://blog.canauri.com/topic/malware)
- [Marriott data breach (1)](https://blog.canauri.com/topic/marriott-data-breach)
- [NASA (1)](https://blog.canauri.com/topic/nasa)
- [NASA Data Breach (1)](https://blog.canauri.com/topic/nasa-data-breach)
- [NCSAM (1)](https://blog.canauri.com/topic/ncsam)
- [National Cyber Security Awareness Month (1)](https://blog.canauri.com/topic/national-cyber-security-awareness-month)
- [Norsk (1)](https://blog.canauri.com/topic/norsk)
- [Norsk Hydro (1)](https://blog.canauri.com/topic/norsk-hydro)
- [PGA (1)](https://blog.canauri.com/topic/pga)
- [Patch Tuesday (1)](https://blog.canauri.com/topic/patch-tuesday)
- [Petya (1)](https://blog.canauri.com/topic/petya)
- [Petya Ransomware (1)](https://blog.canauri.com/topic/petya-ransomware)
- [Quora data breach (1)](https://blog.canauri.com/topic/quora-data-breach)
- [RDP (1)](https://blog.canauri.com/topic/rdp)
- [Remote Desktop Protocol (1)](https://blog.canauri.com/topic/remote-desktop-protocol)
- [Remote workforce (1)](https://blog.canauri.com/topic/remote-workforce)
- [RobbinHood Ransomware (1)](https://blog.canauri.com/topic/robbinhood-ransomware)
- [Robbinhood (1)](https://blog.canauri.com/topic/robbinhood)
- [SEC (1)](https://blog.canauri.com/topic/sec)
- [SME (1)](https://blog.canauri.com/topic/sme)
- [SME Cybersecurity (1)](https://blog.canauri.com/topic/sme-cybersecurity)
- [SamSam (1)](https://blog.canauri.com/topic/samsam)
- [SamSam Ransomware (1)](https://blog.canauri.com/topic/samsam-ransomware)
- [Security Breach Notification Laws (1)](https://blog.canauri.com/topic/security-breach-notification-laws)
- [Small and Medium Enterprises (1)](https://blog.canauri.com/topic/small-and-medium-enterprises)
- [Sorebrect (1)](https://blog.canauri.com/topic/sorebrect)
- [Star Trek (1)](https://blog.canauri.com/topic/star-trek)
- [Syrk ransomware (1)](https://blog.canauri.com/topic/syrk-ransomware)
- [Target (1)](https://blog.canauri.com/topic/target)
- [Vidar (1)](https://blog.canauri.com/topic/vidar)
- [Vidar infostealer (1)](https://blog.canauri.com/topic/vidar-infostealer)
- [Vidar trojan (1)](https://blog.canauri.com/topic/vidar-trojan)
- [WCry (1)](https://blog.canauri.com/topic/wcry)
- [Wana Decryptor (1)](https://blog.canauri.com/topic/wana-decryptor)
- [WanaCry (1)](https://blog.canauri.com/topic/wanacry)
- [WanaDecryptor (1)](https://blog.canauri.com/topic/wanadecryptor)
- [WannaCry 2.0 (1)](https://blog.canauri.com/topic/wannacry-2-0)
- [World Cup (1)](https://blog.canauri.com/topic/world-cup)
- [Yahoo (1)](https://blog.canauri.com/topic/yahoo)
- [Yahoo Data Breach (1)](https://blog.canauri.com/topic/yahoo-data-breach)
- [anatova (1)](https://blog.canauri.com/topic/anatova)
- [anatova ransomware (1)](https://blog.canauri.com/topic/anatova-ransomware)
- [arizona beverages (1)](https://blog.canauri.com/topic/arizona-beverages)
- [atlanta (1)](https://blog.canauri.com/topic/atlanta)
- [automobile (1)](https://blog.canauri.com/topic/automobile)
- [automobile hacking (1)](https://blog.canauri.com/topic/automobile-hacking)
- [azorult trojan (1)](https://blog.canauri.com/topic/azorult-trojan)
- [banking trojan (1)](https://blog.canauri.com/topic/banking-trojan)
- [bentley (1)](https://blog.canauri.com/topic/bentley)
- [bitpaymer ransomware (1)](https://blog.canauri.com/topic/bitpaymer-ransomware)
- [blackmail (1)](https://blog.canauri.com/topic/blackmail)
- [budgeting (1)](https://blog.canauri.com/topic/budgeting)
- [capital one (1)](https://blog.canauri.com/topic/capital-one)
- [capital one data breach (1)](https://blog.canauri.com/topic/capital-one-data-breach)
- [car hacking (1)](https://blog.canauri.com/topic/car-hacking)
- [care (1)](https://blog.canauri.com/topic/care)
- [chicago tribune (1)](https://blog.canauri.com/topic/chicago-tribune)
- [collection (1)](https://blog.canauri.com/topic/collection)
- [collection 1 (1)](https://blog.canauri.com/topic/collection-1)
- [coronavirus cybersecurity (1)](https://blog.canauri.com/topic/coronavirus-cybersecurity)
- [coronavirus phishing (1)](https://blog.canauri.com/topic/coronavirus-phishing)
- [coronavirus ransomware (1)](https://blog.canauri.com/topic/coronavirus-ransomware)
- [crypto (1)](https://blog.canauri.com/topic/crypto)
- [crytocurrency hack (1)](https://blog.canauri.com/topic/crytocurrency-hack)
- [currency (1)](https://blog.canauri.com/topic/currency)
- [cyber insurance (1)](https://blog.canauri.com/topic/cyber-insurance)
- [cybersecurity budgeting (1)](https://blog.canauri.com/topic/cybersecurity-budgeting)
- [cybersecurity coronavirus (1)](https://blog.canauri.com/topic/cybersecurity-coronavirus)
- [cybersecurity predictions (1)](https://blog.canauri.com/topic/cybersecurity-predictions)
- [cybersecurity ventures (1)](https://blog.canauri.com/topic/cybersecurity-ventures)
- [cybersecurity working remotely (1)](https://blog.canauri.com/topic/cybersecurity-working-remotely)
- [dharma (1)](https://blog.canauri.com/topic/dharma)
- [dharma ransomware (1)](https://blog.canauri.com/topic/dharma-ransomware)
- [financial services (1)](https://blog.canauri.com/topic/financial-services)
- [financial services data breach (1)](https://blog.canauri.com/topic/financial-services-data-breach)
- [government cyberattack (1)](https://blog.canauri.com/topic/government-cyberattack)
- [holiday shopping (1)](https://blog.canauri.com/topic/holiday-shopping)
- [hospitals hit with ransomware (1)](https://blog.canauri.com/topic/hospitals-hit-with-ransomware)
- [iEncrypt (1)](https://blog.canauri.com/topic/iencrypt)
- [insider trading (1)](https://blog.canauri.com/topic/insider-trading)
- [insurance (1)](https://blog.canauri.com/topic/insurance)
- [laundering (1)](https://blog.canauri.com/topic/laundering)
- [leak (1)](https://blog.canauri.com/topic/leak)
- [los angeles times (1)](https://blog.canauri.com/topic/los-angeles-times)
- [man in the disk (1)](https://blog.canauri.com/topic/man-in-the-disk)
- [man in the disk attacks (1)](https://blog.canauri.com/topic/man-in-the-disk-attacks)
- [maritime cybersecurity (1)](https://blog.canauri.com/topic/maritime-cybersecurity)
- [maze ransomware (1)](https://blog.canauri.com/topic/maze-ransomware)
- [pensacola florida (1)](https://blog.canauri.com/topic/pensacola-florida)
- [phobos (1)](https://blog.canauri.com/topic/phobos)
- [phobos ransomware (1)](https://blog.canauri.com/topic/phobos-ransomware)
- [quarter 1 2019 ransomware (1)](https://blog.canauri.com/topic/quarter-1-2019-ransomware)
- [raccoon stealer (1)](https://blog.canauri.com/topic/raccoon-stealer)
- [ransomware data breaches (1)](https://blog.canauri.com/topic/ransomware-data-breaches)
- [ransomware defined (1)](https://blog.canauri.com/topic/ransomware-defined)
- [ransomware epidemic (1)](https://blog.canauri.com/topic/ransomware-epidemic)
- [ransomware hits municipalities (1)](https://blog.canauri.com/topic/ransomware-hits-municipalities)
- [ransomware statistics (1)](https://blog.canauri.com/topic/ransomware-statistics)
- [riviera beach ransomware attack (1)](https://blog.canauri.com/topic/riviera-beach-ransomware-attack)
- [ryuk (1)](https://blog.canauri.com/topic/ryuk)
- [ryuk ransomware (1)](https://blog.canauri.com/topic/ryuk-ransomware)
- [scammers (1)](https://blog.canauri.com/topic/scammers)
- [scams targeting holiday shoppers (1)](https://blog.canauri.com/topic/scams-targeting-holiday-shoppers)
- [securities and exchange commission (1)](https://blog.canauri.com/topic/securities-and-exchange-commission)
- [sextortion (1)](https://blog.canauri.com/topic/sextortion)
- [shipping industry (1)](https://blog.canauri.com/topic/shipping-industry)
- [snake ransomware (1)](https://blog.canauri.com/topic/snake-ransomware)
- [social engineering (1)](https://blog.canauri.com/topic/social-engineering)
- [southwire (1)](https://blog.canauri.com/topic/southwire)
- [stop paying the ransom (1)](https://blog.canauri.com/topic/stop-paying-the-ransom)
- [tips for working remotely (1)](https://blog.canauri.com/topic/tips-for-working-remotely)
- [tribune (1)](https://blog.canauri.com/topic/tribune)
- [ursnif (1)](https://blog.canauri.com/topic/ursnif)
- [wall street journal (1)](https://blog.canauri.com/topic/wall-street-journal)
- [what is ransomware (1)](https://blog.canauri.com/topic/what-is-ransomware)
- [working from home (1)](https://blog.canauri.com/topic/working-from-home)
- [working remotely (1)](https://blog.canauri.com/topic/working-remotely)
see all
##### Contact
[415 12th Ave SE, Suite 201 Cedar Rapids, IA 52401](https://www.google.com/maps/place/415+12th+Ave+SE+%23201,+Cedar+Rapids,+IA+52401/@41.9710436,-91.6582952,17z/data=!3m1!4b1!4m5!3m4!1s0x87e4f73f67891f6d:0x38f71e45a9fa7c1f!8m2!3d41.9710436!4d-91.6561065)
[319-383-0165](tel:319-383-0165)
[support@getcryptostopper.com](mailto:support@getcryptostopper.com)
Facebook
Twitter
Linkedin
YouTube
- Products
- [CryptoStopper™](https://www.getcryptostopper.com/cryptostopper/)
- [Endpoint Security](https://www.getcryptostopper.com/tools/endpoint-security/)
- Free Tools
- [Ransomware Simulator](https://www.getcryptostopper.com/ransomware-simulator/)
- [Network Tools](https://www.getcryptostopper.com/free-network-tools/)
- [Ransomware Decryptors](https://www.getcryptostopper.com/ransomware-decryptors/)
- Company
- [About](https://www.getcryptostopper.com/about/)
- [Careers](https://www.getcryptostopper.com/careers/)
- [Contact](https://www.getcryptostopper.com/contact/)
© Copyright WatchPoint Data, All Rights Reserved | [Terms](https://www.getcryptostopper.com/terms)